EU AI Act
Run the EU AI Act on every AI system you operate.
regulation10.com is the compliance plane for EU AI Act duties. You add a system, we run the checks, you keep the proof.
- For providers and deployers of high-risk AI
- The EU AI Act asks for proof
Assess your AI systemSee a live demo
No signup for either. The demo runs on sample data.
What happens to a system
Classify
Risk class and duties
Prove
Assessment, notice, sealed trail
Monitor
Live estate, drift and incidents
File
Serious-incident report
Problem
Why this is hard
Under the EU AI Act you must show how each AI system is run. A regulator can ask for proof. A clean assessment, a clear notice, and a signed audit trail is that proof. We make it on the day you ship the system.
Many ordinary systems count as high risk
Annex III lists the uses that are high risk. Hiring, credit, education and essential services are on it. Teams find out late.
EU AI Act, Annex III
The penalties are set in the text
Article 99 sets fines up to 35 million euro or 7 per cent of worldwide annual turnover, whichever is higher.
EU AI Act, Article 99
You must be able to show your work
A provider has to keep technical documentation and logs, and hand them to an authority on request. Saying you complied is not enough.
EU AI Act, Articles 11, 12 and 18
Product
How it works
Where the information goes, and what comes back.
- Step 1: Your AI systems. The models and services you run. Your cloud account.
- Step 2: Out-of-band capture. Taken beside the workload, not on the request path. Your cloud account.
- Step 3: Classify and draft. Risk class, duties and citations under the EU AI Act. regulation10.
- Step 4: Tamper-evident record. Each decision is hashed into a chain. regulation10.
- Step 5: Evidence pack. One signed export, ready when a regulator asks. Yours to hand over.
Continuous capture is Sentinel, a closed beta on the Enterprise and Sovereign plans. It is not open to enrol yet.
- Classify
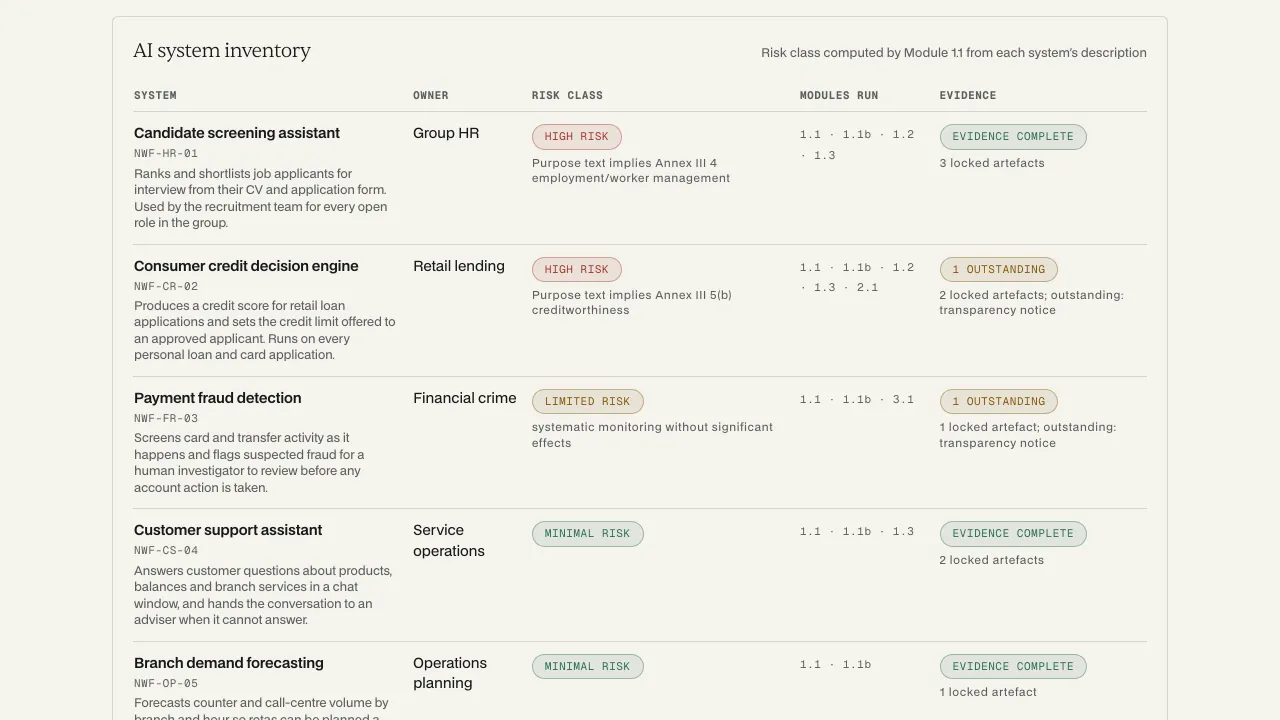
Know the risk class before you build
Describe a system and get its EU AI Act risk class, the duties that follow, and the citation behind each one. It takes seconds and needs no signup.
- Prove
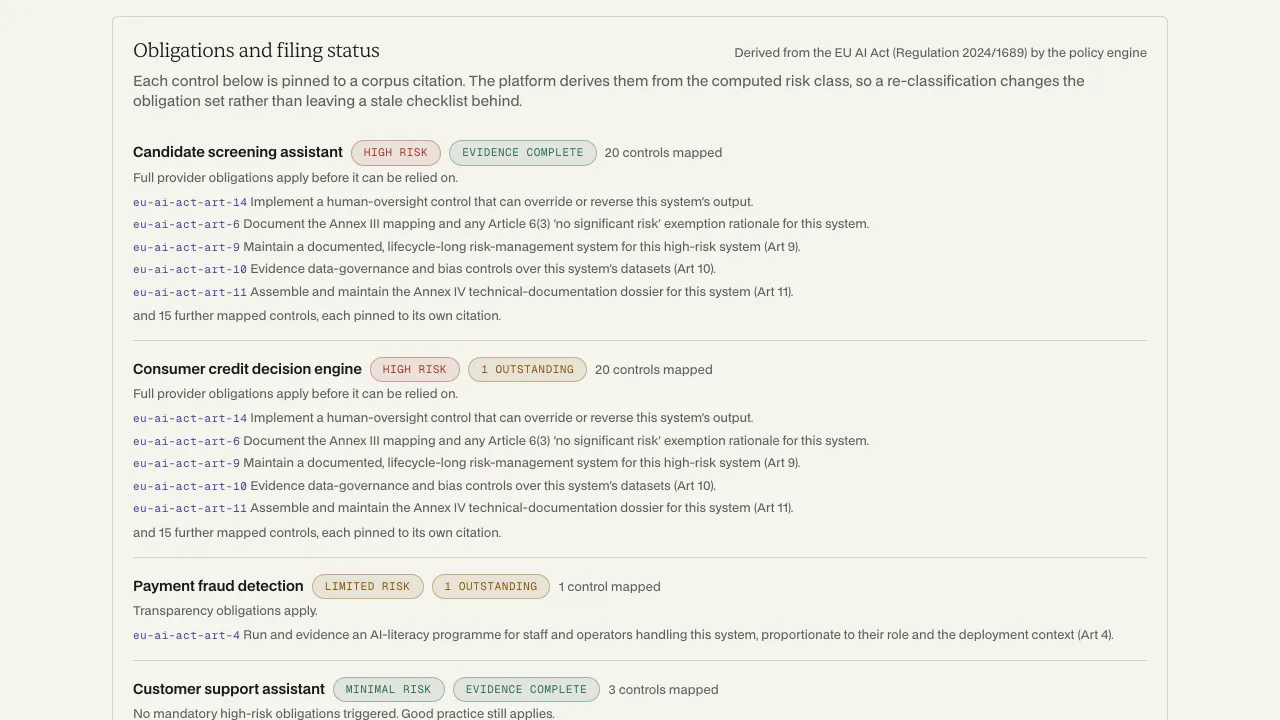
Turn the work into evidence
We draft the assessment and the transparency notice, then seal each decision into a tamper-evident trail. You hand over one signed pack.
- Monitor
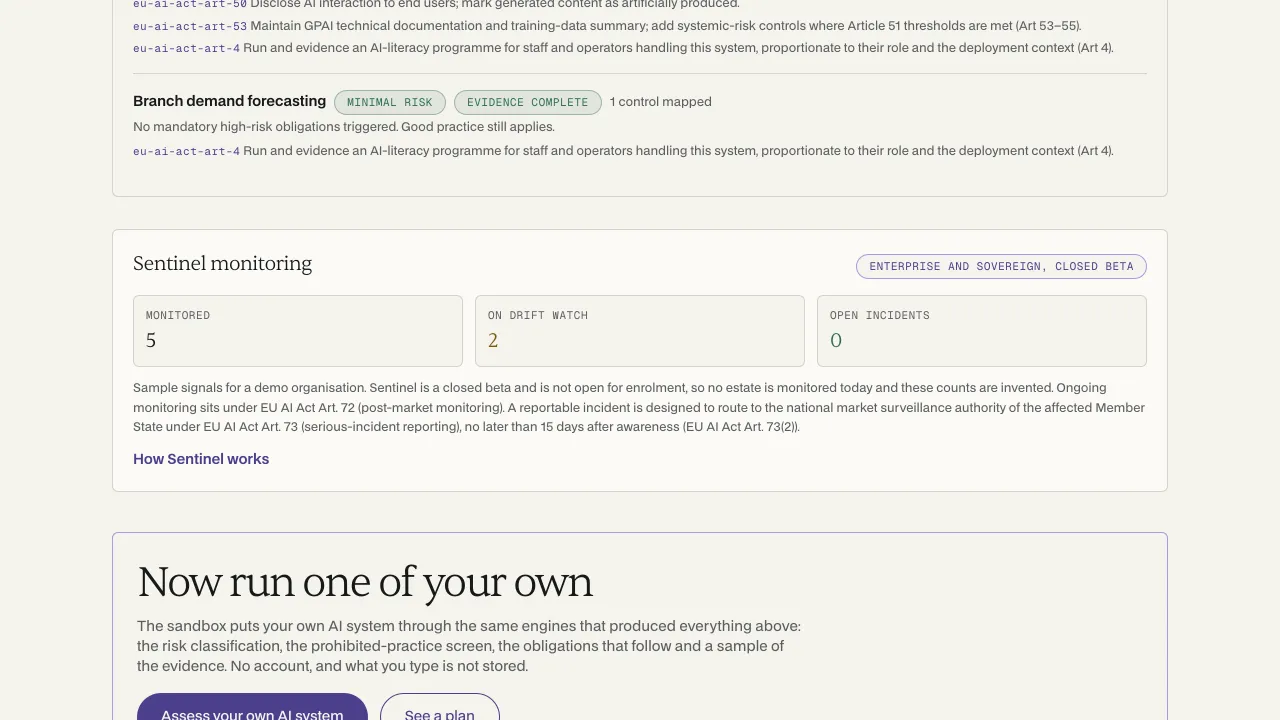
Watch it while it runs
Sentinel is built to watch an estate and raise the filing when something changes. It is a closed beta, not open for enrolment yet.
What each capability gives you
- Risk classification. Know which duties apply before you build, not after an audit.
- Assessment generator. Draft the EU AI Act assessment your reviewer expects, not from a blank page.
- Transparency notices. Meet the notice duty in plain words your users can read.
- Bias and security checks. Find fairness and security gaps before the system ships.
- Tamper-evident audit trail. Keep signed proof of each decision, ready on the day you are asked.
- Evidence pack. Hand over one signed pack, not a scramble to gather proof.
- Framework cross-walk. Reuse one control set across ISO, NIST, and OECD.
Solutions
The sectors this is built for
Professional services
Insurance
Legal
Proof
Why you can rely on it
Evidence-grade audit trail
Each decision is hashed into a chain and checkpointed, so a later edit shows up. The trail is exportable for an auditor.
Stated data residency
We name the region your data sits in and the one narrow processing step that runs elsewhere. The detail is below.
Regime-correct filing
We route a serious incident to the reporting duty the EU AI Act sets, not to a generic form.
We publish what we cannot yet prove
The trust page dates every piece of evidence we hold. It names the gaps we have not closed, and the claims our own probes cannot yet establish.
See the evidence behind each claim
Where your data lives
Your data resides in Azure's Sweden Central region, an EU/EEA data zone. Model inference runs on Azure OpenAI; content is processed in flight to answer a request and is not retained by the model. Your data is encrypted in transit and at rest.
References
Customer references
We have no published customer references yet, and we will not invent one. Read the full position
Get started
Assess your AI system
Describe one system and see its risk class, the duties that follow, and the evidence you would need. No signup.